
Cybersecurity is essential for protecting sensitive information, maintaining reliable systems, and preventing unauthorized access to digital resources. Organizations rely on different security principles to protect their data from cyber threats, operational failures, and accidental damage. One of the most important concepts in information security is the CIA triad, which provides a foundation for developing effective cybersecurity strategies.
The CIA triad stands for Confidentiality, Integrity, and Availability. These three principles help organizations protect information, maintain data accuracy, and ensure that important systems remain accessible when needed. Understanding what CIA means in cybersecurity is useful for students, IT professionals, business owners, and anyone interested in learning how digital information is protected.
This guide explains the CIA triad in cybersecurity, how each principle works, and why it matters for modern information security. You will also discover practical examples, common threats, and security measures that organizations use to maintain confidentiality, integrity, and availability across their systems and networks.
What Is CIA in Cyber Security?
CIA in cybersecurity refers to the CIA triad, a fundamental information security model consisting of Confidentiality, Integrity, and Availability. These three principles guide organizations when designing security policies, protecting sensitive information, and managing digital systems. The CIA triad provides a structured approach to understanding what information needs protection and how different security controls support overall cybersecurity objectives.
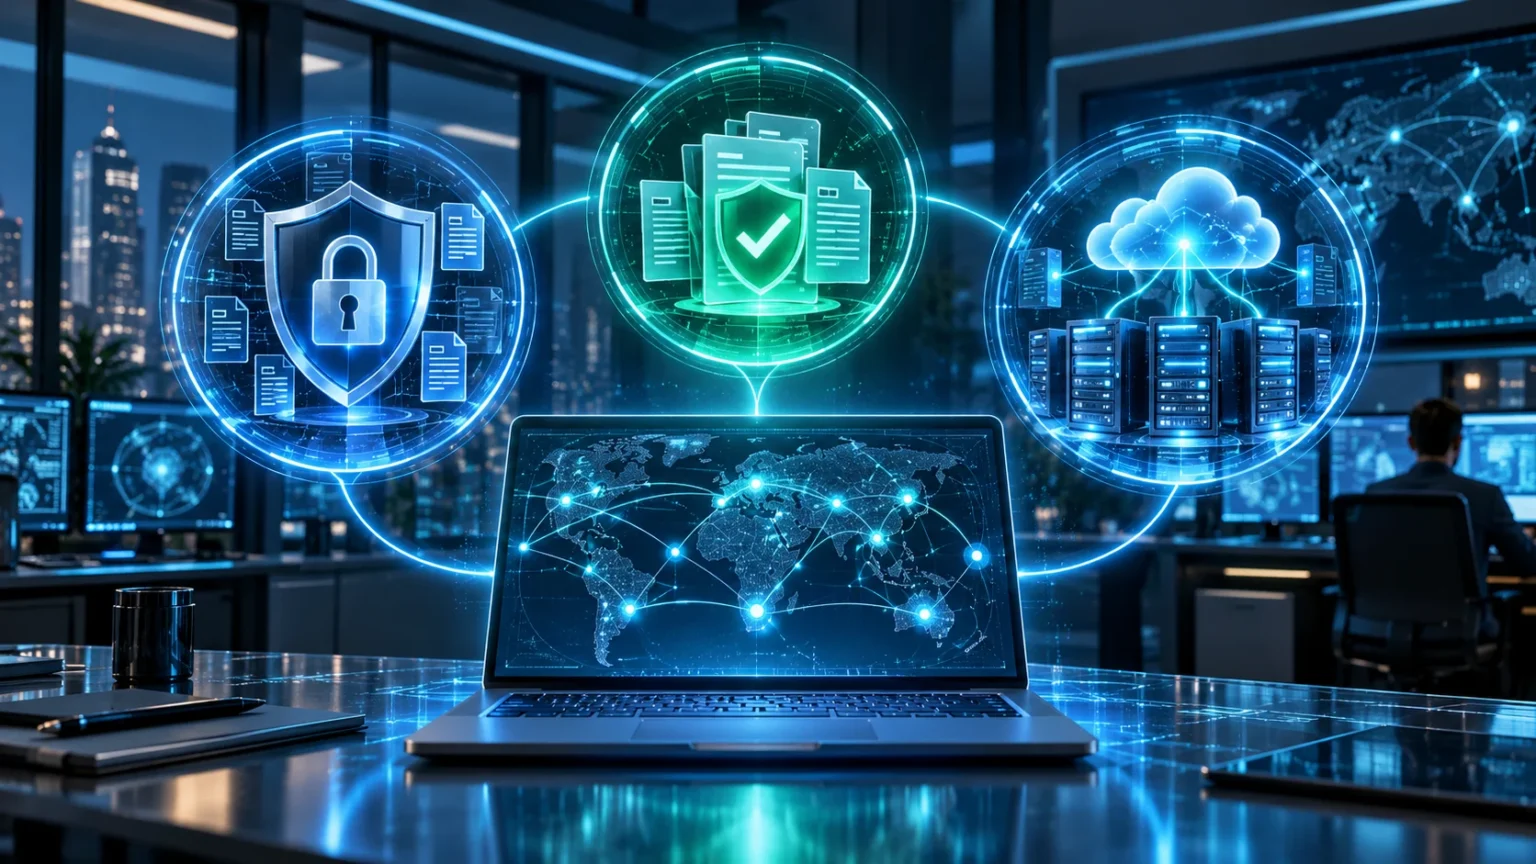
Confidentiality focuses on preventing unauthorized access to information, while integrity ensures that data remains accurate and trustworthy. Availability ensures that authorized users can access information and systems whenever they are needed. Together, these principles help organizations protect valuable digital assets and reduce the likelihood of security incidents that could disrupt normal business operations.
The CIA triad is widely used in cybersecurity risk assessments, information security management, and organizational security planning. Security professionals apply this framework when evaluating threats, developing access controls, and selecting appropriate protective technologies. Although cybersecurity includes many additional concepts, the CIA model remains a useful foundation for understanding how organizations maintain secure and dependable information systems.
What Does CIA Stand for in Cybersecurity?
The abbreviation CIA stands for Confidentiality, Integrity, and Availability, representing three essential goals of information security. Each component addresses a different aspect of protecting information and technology resources. Understanding these individual security objectives helps organizations identify weaknesses, prioritize protective measures, and establish balanced cybersecurity strategies that support both data protection and reliable business operations.
Confidentiality protects sensitive information from unauthorized disclosure, integrity protects information from improper modification, and availability ensures that systems remain accessible to authorized users. These objectives are interconnected because a weakness in one area can affect the overall security of an organization. Effective cybersecurity planning considers all three elements rather than concentrating on a single security concern.
For example, an online banking platform must protect customer account information, ensure transaction records remain accurate, and provide reliable access to banking services. If any of these objectives fail, customers may experience financial risks or service interruptions. The CIA triad helps organizations recognize these requirements and establish security controls appropriate to their operational needs.
Understanding Confidentiality in the CIA Triad
Confidentiality is the cybersecurity principle that ensures sensitive information is accessible only to authorized individuals, applications, and systems. It protects personal information, financial records, business documents, and confidential communications from unauthorized disclosure. Organizations maintain confidentiality through security policies, technical safeguards, and employee awareness programs designed to reduce unnecessary exposure of valuable information.
Access controls are among the most important measures used to maintain confidentiality. Organizations can restrict sensitive information based on employee responsibilities, verified identities, and legitimate business requirements. Strong authentication, appropriate permissions, and secure account management help prevent unauthorized individuals from accessing information they do not need for their assigned responsibilities.
Encryption provides another important layer of confidentiality by converting readable information into protected data that requires an appropriate key to decrypt. This technology helps protect sensitive information during storage and transmission across networks. However, encryption should work alongside effective access management, secure devices, and employee training to provide meaningful protection against information disclosure.
Understanding Integrity in Cybersecurity
Integrity ensures that information remains accurate, complete, consistent, and protected against unauthorized or improper changes. Organizations depend on reliable information when making decisions, processing financial transactions, and providing digital services. If important data becomes corrupted or altered without authorization, the resulting errors can affect operations, customer confidence, and the reliability of business systems.
Data integrity can be compromised through malicious activity, software defects, human mistakes, or hardware failures. For example, an unauthorized change to a payment amount could create incorrect financial records and cause significant operational problems. Protecting integrity requires organizations to control who can modify information and maintain reliable methods for identifying unexpected changes.
Security professionals use techniques such as cryptographic hashes, digital signatures, validation checks, and audit logs to support information integrity. These controls can help detect unauthorized changes and establish accountability for important activities. Regular testing, version management, and carefully maintained backups further support the accuracy and reliability of organizational information throughout its lifecycle.
Understanding Availability in the CIA Triad
Availability means that information systems, applications, and digital resources remain accessible to authorized users when required. Even properly protected information becomes less useful if employees or customers cannot access it when needed. Organizations therefore prioritize reliable infrastructure, dependable network connections, and operational procedures that reduce unnecessary interruptions to essential services.
Availability can be affected by hardware failures, software problems, power outages, network disruptions, and cyberattacks. Distributed denial-of-service attacks, for example, can overwhelm online services and prevent legitimate users from accessing them. Businesses must consider these risks when planning infrastructure capacity, maintaining equipment, and establishing procedures for responding to unexpected service interruptions.
Redundant systems, routine maintenance, monitoring tools, and disaster recovery planning can help organizations maintain availability. Data backups and recovery procedures also support the restoration of important services after failures or security incidents. The objective is not to guarantee that systems will never experience downtime, but to minimize disruptions and restore functionality within acceptable timeframes.
Why Is the CIA Triad Important in Cybersecurity?
The CIA triad is important because it provides a straightforward framework for identifying and managing information security risks. Without clearly defined security objectives, organizations may invest in protective technologies without understanding which risks they address. The CIA model helps security teams evaluate vulnerabilities and develop controls that support essential business operations and information protection requirements.
Organizations also use the CIA triad to establish security priorities according to the sensitivity and importance of their digital assets. For example, confidentiality may receive greater emphasis when protecting private customer records, while availability may be critical for emergency communication systems. Integrity becomes especially important when inaccurate data could lead to serious financial or operational consequences.
Another benefit of the CIA framework is its usefulness for communication between technical teams, managers, and business stakeholders. These three familiar concepts make complex security concerns easier to explain and evaluate. By connecting cybersecurity decisions with confidentiality, integrity, and availability, organizations can develop more consistent policies and understand how security investments support business objectives.
Real-Life Examples of the CIA Triad
Healthcare organizations provide practical examples of how the CIA triad supports information security. Patient records must remain confidential to protect personal information, accurate to support appropriate treatment decisions, and available to authorized healthcare professionals. Security measures such as access restrictions, audit logging, and reliable system recovery procedures help healthcare providers maintain these important objectives.
Online banking systems offer another example of the CIA triad in daily operations. Confidentiality protects account credentials and financial details from unauthorized disclosure, while integrity helps ensure that transaction records remain accurate. Availability allows customers to access banking services, review balances, and complete legitimate transactions through dependable digital platforms.
Educational institutions also rely on the CIA principles when managing student information and online learning platforms. Confidentiality protects personal records, integrity prevents improper changes to grades, and availability supports access to digital learning resources. These examples demonstrate that the CIA triad applies across industries and helps organizations protect information while maintaining reliable services.
Common Threats to Confidentiality, Integrity, and Availability
Confidentiality threats often involve phishing, stolen credentials, accidental information disclosure, and unauthorized access to sensitive systems. Attackers may attempt to obtain login details or exploit weak access controls to view protected information. Organizations can reduce these risks through employee training, strong authentication, appropriate permissions, and consistent monitoring of unusual account activity.
Integrity threats involve unauthorized modifications, malicious software, accidental deletion, and errors in data processing. Corrupted information can undermine financial records, operational reporting, and important business decisions. Security measures such as access restrictions, validation checks, audit trails, and carefully managed changes help organizations recognize integrity problems and prevent unauthorized alterations.
Availability threats include ransomware, denial-of-service attacks, infrastructure failures, and disruptions caused by natural disasters. These incidents may prevent employees and customers from accessing essential resources. Organizations can improve resilience through redundant infrastructure, tested recovery plans, system monitoring, and protective network controls that reduce the impact of unexpected interruptions.
How to Implement the CIA Triad in an Organization
Implementing the CIA triad begins with identifying important information assets and understanding how they support business operations. Organizations should classify information based on sensitivity, operational importance, and potential consequences if security fails. This process helps determine which systems require stronger access restrictions, more reliable recovery arrangements, or additional controls to preserve data accuracy.
After identifying critical assets, organizations should establish security policies that address confidentiality, integrity, and availability. These policies may include account management requirements, approved data handling procedures, backup schedules, and incident response responsibilities. Employees should understand the policies relevant to their roles and receive appropriate training to recognize security concerns during everyday activities.
Implementation also requires regular evaluation because cybersecurity risks change as organizations adopt new technologies and business processes. Security teams should assess vulnerabilities, review access permissions, test recovery procedures, and investigate suspicious activities. Continuous improvement helps ensure that security measures remain appropriate for the organization’s risk exposure, resources, and operational requirements.
Security Technologies That Support the CIA Triad
Different cybersecurity technologies support the three components of the CIA triad in complementary ways. Identity and access management solutions help protect confidentiality by controlling who can access sensitive resources. Authentication systems, encryption technologies, and data loss prevention tools can further reduce the possibility of unauthorized information disclosure across organizational systems.
Integrity-focused technologies include digital signatures, cryptographic hashes, file integrity monitoring, and database validation mechanisms. These tools help detect unexpected changes and support trustworthy information processing. Audit logging and version control systems can also help organizations understand when important modifications occurred and whether those changes were authorized.
Availability is supported by technologies such as load balancing, redundant infrastructure, backup platforms, and service monitoring systems. Organizations may also use network protection services to reduce disruption from excessive or malicious traffic. Selecting appropriate technologies requires understanding business priorities because no single cybersecurity product can fully address every confidentiality, integrity, and availability requirement.
CIA Triad vs Other Cybersecurity Principles
The CIA triad provides three foundational security objectives, but modern cybersecurity involves additional principles and practices. Authentication verifies claimed identities, authorization determines permitted actions, and accountability connects activities with responsible users or systems. These concepts support the CIA objectives by helping organizations manage access, investigate incidents, and establish trustworthy security operations.
Non-repudiation is another important information security concept that helps provide evidence about the origin or approval of certain actions. Digital signatures, for example, can support verification of signed electronic transactions when properly implemented. Although non-repudiation is not one of the three CIA components, it complements integrity and accountability in many security-sensitive environments.
Cybersecurity frameworks may also address privacy, resilience, risk governance, and secure system development. These broader areas recognize that protecting organizations requires more than preventing unauthorized access or system outages. The CIA triad remains valuable because it establishes fundamental security goals that can guide more comprehensive cybersecurity programs and organizational risk management activities.
Balancing Confidentiality, Integrity, and Availability
Organizations must balance the three CIA principles because security decisions can affect multiple objectives simultaneously. For example, extremely restrictive access controls might protect confidentiality but create difficulties for employees who need information urgently. Effective security design considers operational requirements and establishes appropriate safeguards without introducing unnecessary barriers to legitimate work.
The appropriate balance varies depending on the type of information, business environment, and potential consequences of security failures. A public information website may prioritize availability, while a confidential research system may require particularly strong access protection. Financial transaction systems often need rigorous integrity controls alongside reliable availability and confidentiality safeguards.
Risk assessments help organizations determine how to balance these competing requirements. Security teams can evaluate threats, estimate potential business impacts, and select controls that provide appropriate protection. A risk-based approach supports practical decisions while recognizing that cybersecurity requires ongoing adjustments as technologies, business priorities, and threat conditions evolve.
CIA Triad Best Practices for Better Information Security
One effective practice is applying the principle of least privilege across user accounts and business applications. Employees should receive only the access necessary to perform their responsibilities, and permissions should be reviewed regularly. This approach reduces unnecessary information exposure and limits opportunities for unauthorized modifications that could threaten confidentiality and integrity.
Organizations should also maintain reliable backups, establish tested recovery procedures, and monitor important systems for unusual activity. Regular software updates and vulnerability management can reduce exposure to known security weaknesses. Combining preventive safeguards with detection and recovery capabilities helps protect information while supporting the continued availability of critical services.
Employee awareness is equally important because many security incidents involve mistakes, misleading messages, or inappropriate handling of information. Practical training can help staff recognize suspicious requests, report potential incidents, and follow approved data protection procedures. When technical measures and responsible employee behavior work together, organizations can strengthen all three components of the CIA triad.
Career Importance of the CIA Triad in Cybersecurity
Understanding the CIA triad is valuable for students and professionals beginning careers in information security. It introduces essential cybersecurity terminology and explains the objectives behind common security controls. Professionals working in network security, cloud security, governance, and risk management regularly consider confidentiality, integrity, and availability when evaluating systems and recommending improvements.
Cybersecurity analysts use CIA principles when assessing vulnerabilities, investigating incidents, and prioritizing security risks. For example, an analyst reviewing a database vulnerability may consider whether it could expose private information, alter records, or interrupt service availability. This approach helps connect technical weaknesses with meaningful consequences for businesses and their customers.
The CIA triad is also relevant when studying cybersecurity fundamentals and preparing for entry-level security certifications. Understanding its practical applications helps learners interpret security policies, access management practices, and risk assessment scenarios. Developing this foundation can make advanced topics such as threat modeling, security architecture, and incident response easier to understand.
Conclusion
The CIA triad in cybersecurity stands for Confidentiality, Integrity, and Availability, three essential principles that support effective information security. Confidentiality prevents unauthorized disclosure, integrity protects the accuracy of information, and availability ensures that authorized users can access important resources. Together, these principles provide a practical foundation for understanding security risks and protecting digital systems.
Organizations use the CIA triad to guide cybersecurity policies, evaluate threats, and select appropriate security technologies. Measures such as encryption, access controls, data validation, system monitoring, and disaster recovery planning help maintain these objectives. Applying the CIA principles consistently can improve operational reliability, protect sensitive information, and strengthen overall organizational security.
Understanding what CIA means in cybersecurity is useful for beginners, business owners, students, and experienced IT professionals. The framework offers a simple way to evaluate security decisions and recognize how different protections work together. By prioritizing confidentiality, integrity, and availability according to actual risks, organizations can build more resilient and trustworthy information systems.
Frequently Asked Questions (FAQs)
1. What does CIA stand for in cybersecurity?
CIA stands for Confidentiality, Integrity, and Availability. These three cybersecurity principles help organizations prevent unauthorized information disclosure, protect data accuracy, and maintain reliable access to important digital systems.
2. What is the main purpose of the CIA triad?
The main purpose of the CIA triad is to guide information security planning and risk management. It helps organizations protect sensitive data, prevent improper modifications, and ensure essential systems remain accessible.
3. What is an example of the CIA triad?
Online banking demonstrates the CIA triad by protecting customer information through confidentiality, maintaining accurate transaction records through integrity, and providing reliable banking services through availability.
4. Which is the most important component of the CIA triad?
No single component is universally most important. The priority depends on the system, information sensitivity, and operational requirements. Organizations should balance all three principles according to their specific security risks.
5. Is the CIA triad still relevant in modern cybersecurity?
Yes, the CIA triad remains a foundational cybersecurity model. Organizations continue using confidentiality, integrity, and availability to evaluate security risks, develop protective controls, and support reliable information systems.