
Artificial intelligence is generally safe for many everyday tasks when people use reliable tools and understand their limitations. Millions of users rely on AI for writing, research, brainstorming, customer support, data analysis, and productivity. However, AI safety depends on the system being used, the information provided to it, and how much trust users place in its output.
AI does not think, understand consequences, or verify information in the same way a human expert does. Even advanced systems can produce incorrect statements, misleading recommendations, or responses that sound confident despite containing errors. Users should therefore treat AI as an assistant rather than an unquestionable source of truth, especially when decisions involve health, finances, legal matters, or personal safety.
The safest approach combines AI convenience with human judgment. Users can benefit from faster workflows and easier access to information while still checking important facts and protecting sensitive data. Understanding common AI risks makes it easier to decide which tasks can be automated comfortably and which situations deserve additional review, professional guidance, or stronger privacy precautions.
What Are the Biggest Risks of Artificial Intelligence?
One major AI risk is inaccurate information. Generative AI systems predict useful responses based on patterns in data, which means they can occasionally invent details, confuse facts, or misinterpret a question. These errors are often called hallucinations, and they become particularly dangerous when someone accepts a generated answer without checking whether the underlying information is correct.
Privacy is another important concern because users may share personal, confidential, or business information while interacting with AI tools. Depending on the service and its settings, uploaded content may be processed, stored, or handled in ways users do not fully understand. People should review privacy policies and avoid entering sensitive information unless they know how the platform protects it.
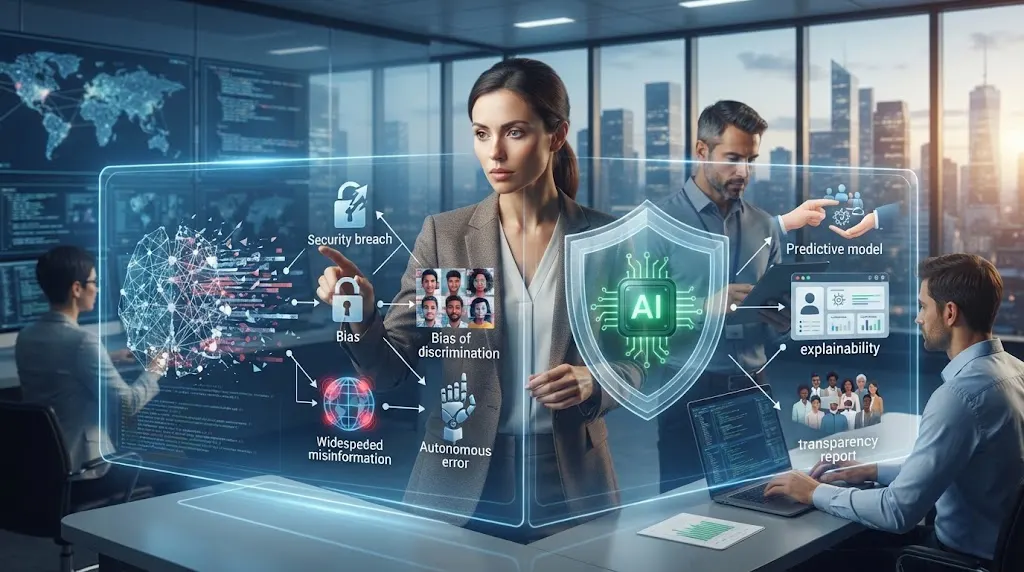
AI can also amplify bias, support misinformation, or be misused for scams and manipulation. Criminals may use generative technology to produce convincing phishing emails, fake images, cloned voices, or misleading content at scale. These problems do not mean AI is inherently unsafe, but they show why responsible development, security controls, digital literacy, and cautious use are increasingly important.
Can AI Give Wrong or Misleading Information?
Yes, AI can generate answers that are inaccurate even when the wording appears polished and convincing. Large language models are built to produce likely sequences of text rather than guarantee that every statement is factually correct. This means an answer can sound authoritative while containing incorrect dates, fabricated statistics, misunderstood concepts, or unsupported assumptions.
The risk tends to increase when questions are highly specialized, ambiguous, extremely recent, or dependent on information the system cannot access. Users may also receive weaker answers when they provide incomplete context. Asking clear questions and requesting explanations can improve usefulness, but no prompting technique can completely eliminate the possibility of an incorrect AI-generated response.
Important information should therefore be verified before it influences serious decisions. Compare key claims with reliable original sources, official documentation, or qualified professionals when appropriate. AI can accelerate research and simplify complicated information, but users should maintain healthy skepticism instead of assuming that confident language automatically means an answer is accurate.
How AI Can Affect Privacy and Personal Data
AI tools often require users to provide prompts, documents, images, recordings, or other information to generate useful results. This creates privacy concerns when people accidentally share confidential business details, customer information, passwords, medical records, financial data, or personally identifiable information. Once sensitive material enters an online platform, users may have less control over how it is handled.
Before using an AI service, check what information the platform collects and how long it may retain submitted content. Business users should pay particular attention to enterprise privacy controls, data-processing agreements, and administrative settings. Organizations may also need internal policies explaining which types of information employees are allowed to enter into public or third-party AI systems.
A practical rule is to provide only the information necessary to complete the task. Remove identifying details where possible, anonymize examples, and avoid sharing passwords or confidential credentials. Privacy-conscious habits allow people to use AI productively without unnecessarily exposing personal or organizational data that could cause problems if accessed, retained, or shared unexpectedly.
AI Bias and Fairness Concerns
AI systems learn from large collections of human-created data, and human information can contain social, cultural, historical, and demographic biases. As a result, an AI model may sometimes reproduce unfair assumptions or generate responses that treat groups differently. Bias can be especially concerning when AI influences hiring, lending, education, healthcare, or other decisions affecting real people.
Bias is not always obvious. A system may appear neutral while consistently recommending certain candidates, interpreting language differently, or producing uneven results for particular populations. Developers can test models and introduce safeguards, but eliminating every source of bias is difficult because fairness itself can involve complicated social and contextual judgments.
Users should be especially cautious when AI output is used to evaluate people. Automated recommendations should not become the only basis for high-impact decisions without appropriate oversight. Human review, diverse testing data, transparent processes, and opportunities to challenge automated outcomes can help reduce the risk of unfair treatment caused by flawed algorithms or biased training patterns.
AI Scams, Deepfakes, and Misinformation
Generative AI has made it easier to create realistic text, images, audio, and video. While these capabilities support creativity and productivity, they can also help scammers produce convincing fake content. Phishing messages can become more personalized, fake customer service interactions can appear legitimate, and cloned voices may imitate people someone already knows and trusts.
Deepfakes create another challenge because manipulated media can make individuals appear to say or do things that never happened. As synthetic content becomes more realistic, users may find it harder to determine whether a video, photograph, or recording is authentic. This increases the importance of checking context and verifying unusual claims before reacting or sharing information.
Users should be suspicious of unexpected requests involving money, passwords, verification codes, or urgent action. If a message supposedly comes from a family member, employer, bank, or public figure, verify it through another trusted channel. AI makes deception easier to scale, but basic security habits remain highly effective against many technology-assisted scams.
Is AI Safe for Work and Business Use?
AI can be valuable for businesses when organizations establish clear guidelines around acceptable use. Employees may use AI for drafting emails, summarizing documents, brainstorming campaigns, analyzing information, or automating routine processes. These applications can save significant time, but businesses need to understand what information is entering the system and who remains responsible for the final output.
Companies should decide which tasks require human review and which information should never be entered into public AI tools. Legal contracts, customer data, confidential strategies, unreleased product information, and proprietary code may require stronger protection. Using approved platforms with business-level security features can reduce some risks compared with employees independently choosing unknown services.
Organizations also benefit from designing responsible processes instead of adding AI randomly to every task. A carefully planned AI workflow can automate repetitive work while keeping humans involved where judgment, verification, or sensitive information matters. Clear responsibilities make automation more useful without sacrificing accountability, security, or quality control.
Is AI Safe for Students and Everyday Users?
AI can be helpful for students when used as a learning assistant rather than a replacement for thinking. It can explain difficult concepts, create practice questions, suggest study plans, summarize notes, and help users explore unfamiliar topics. The main risk appears when learners accept generated answers without understanding the subject or checking whether the information is correct.
Students also need to follow school or university policies regarding AI-generated work. Submitting automatically generated assignments as original work may violate academic rules and can prevent students from developing important writing, reasoning, and research skills. Using AI to clarify concepts or receive feedback is usually more educational than asking it to complete every task.
Everyday users face similar tradeoffs. AI can simplify planning, writing, troubleshooting, and creative projects, but users should remain responsible for decisions made from its suggestions. The more serious the consequences of an incorrect answer, the more important independent verification becomes. Convenience should increase productivity without removing the judgment necessary to recognize questionable advice.
Can AI Be Trusted With Important Decisions?
AI can assist decision-making by organizing information, identifying patterns, comparing options, and highlighting factors people may want to consider. However, trusting it to make major decisions independently is risky because AI systems can misunderstand context or rely on incomplete information. They may also lack access to personal circumstances that significantly affect the best choice.
High-stakes areas deserve particular caution. Medical diagnoses, legal disputes, investment decisions, employment choices, and financial planning can have lasting consequences if based on inaccurate information. AI can help users prepare questions or understand terminology, but qualified professionals and authoritative sources should remain central when specialized expertise is required.
The safest model is human-in-the-loop decision-making, where AI provides useful analysis while people retain responsibility for interpretation and action. This approach captures the speed of automation without assuming machines are infallible. AI becomes more valuable when its recommendations are treated as input for consideration rather than automatic instructions that must always be followed.
How to Use AI More Safely
Start by choosing established AI services with clear privacy policies, security practices, and user controls. Avoid unknown tools that request unnecessary personal information or excessive account permissions. When using new platforms, consider whether the convenience they provide is worth the level of access they request to your files, messages, contacts, or other sensitive information.
Users should also verify important outputs and avoid treating AI-generated content as automatically factual. Check numbers, names, quotes, legal requirements, medical information, and other consequential details against trusted sources. When AI is used for professional writing or analysis, a final human review can catch errors, inappropriate assumptions, and missing context before the material reaches other people.
Finally, maintain strong general cybersecurity habits. Use unique passwords, enable multifactor authentication where available, update software, and remain skeptical of unusual messages or links. AI introduces new forms of digital risk, but many protective habits are familiar. Careful data sharing, verification, secure accounts, and critical thinking make everyday AI use considerably safer.
What the Future of AI Safety May Look Like
AI safety will likely become more important as artificial intelligence becomes integrated into search engines, workplaces, education, healthcare, devices, and online services. Developers are increasingly building safeguards designed to limit harmful outputs and protect users. Governments and organizations are also exploring rules and standards for transparency, accountability, privacy, and responsible AI deployment.
Technical improvements may reduce certain problems, but no system is likely to become completely risk-free. More capable AI may solve existing weaknesses while introducing new challenges that are difficult to predict. Continuous testing, independent evaluation, security research, and responsible deployment will therefore remain necessary as models become more powerful and widely used.
Users will also play an important role in AI safety. Understanding that generated content can be wrong, manipulated, or incomplete helps people make better decisions. Digital literacy will increasingly include knowing when to use AI, what information to protect, how to recognize synthetic media, and when human expertise should take priority over automated recommendations.
Conclusion
AI can be safe and highly useful when people understand what the technology can and cannot reliably do. The biggest risks include misinformation, privacy concerns, biased outputs, deepfakes, scams, and overreliance on automated recommendations. These risks are manageable in many everyday situations when users apply sensible security practices and maintain appropriate human oversight.
The most important habit is avoiding blind trust. AI-generated information should be checked when accuracy matters, and sensitive data should be shared only when users understand how a platform handles it. Businesses should also create clear AI policies so employees know which tools are approved and which decisions still require human review.
Artificial intelligence will continue becoming part of everyday digital life, making AI safety an ongoing responsibility rather than a one-time concern. Users do not need to avoid AI completely to protect themselves. Learning how to verify outputs, protect personal information, recognize manipulation, and use human judgment makes it possible to benefit from AI while reducing unnecessary risk.
FAQs
Is AI completely safe?
No technology is completely risk-free. AI is generally safe for many everyday tasks, but inaccurate information, privacy issues, scams, bias, and misuse mean users should apply appropriate caution.
Is it safe to share personal information with AI?
Avoid entering highly sensitive information unless you understand the platform’s privacy and data-handling policies. Passwords, financial credentials, private records, and confidential business information should generally receive extra protection.
Can AI give dangerous advice?
AI can occasionally provide incorrect or inappropriate recommendations. Advice involving health, law, finance, personal safety, or other high-stakes situations should be checked with reliable sources or qualified professionals.
Are AI-generated images and videos safe to trust?
Not automatically. Generative AI can produce convincing fake images, recordings, and videos, so unusual or consequential media should be verified before you assume it represents a real event or person.
How can I protect myself while using AI?
Use reputable tools, limit sensitive data sharing, verify important information, and maintain strong account security. Treat AI as a helpful assistant rather than an unquestionable authority for important decisions.