
What Is Lateral Movement in Cybersecurity?
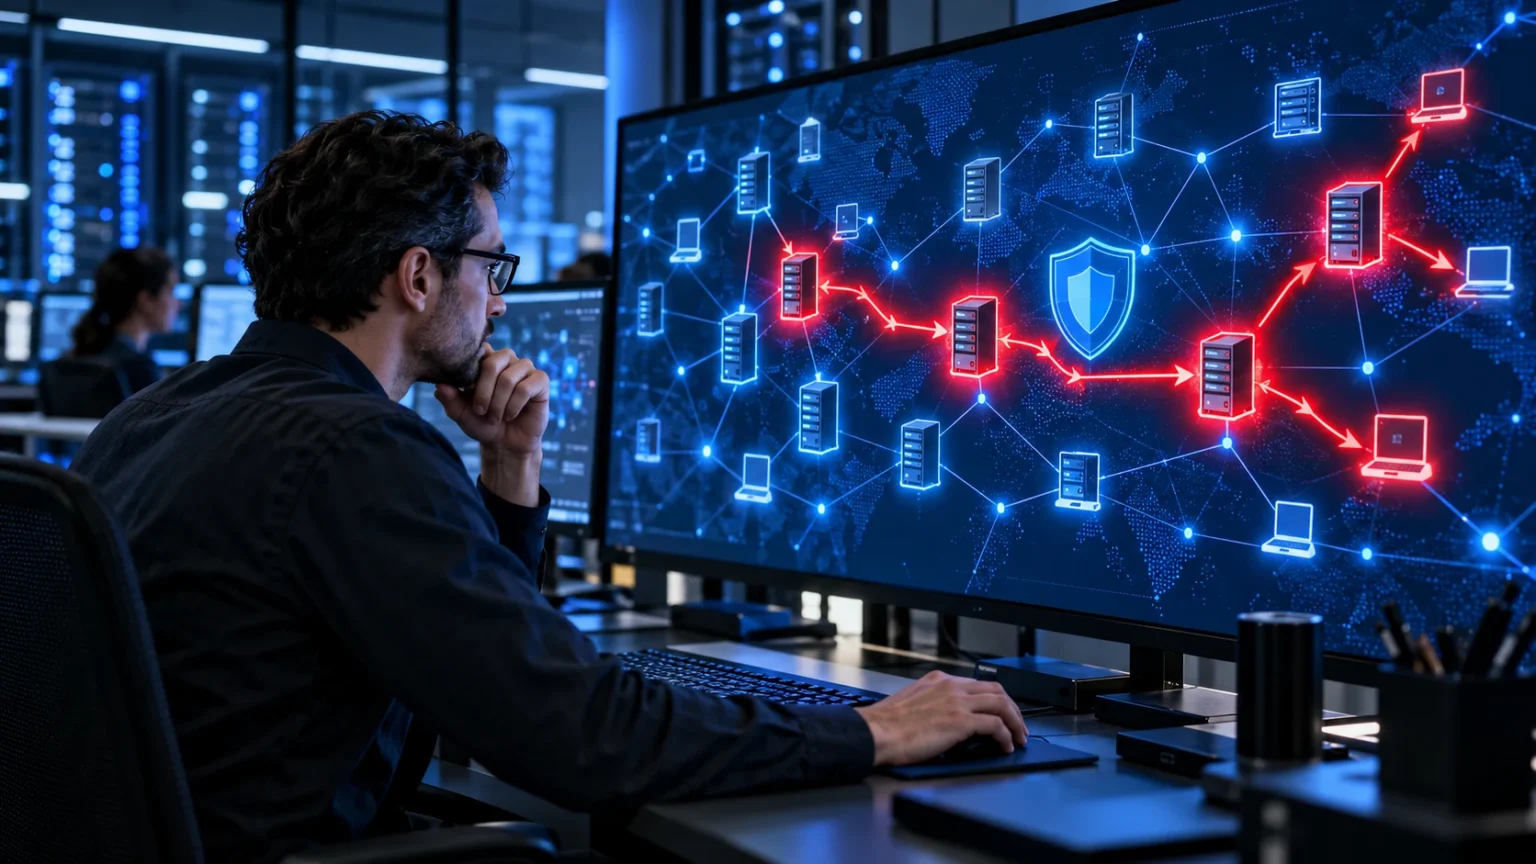
Lateral movement is the set of actions an attacker uses to move from one compromised account, device, or system to another inside a network. It often happens after an initial breach, when the attacker tries to reach more valuable systems, gain broader access, or locate sensitive information.
The term describes movement within an environment, rather than the first step used to get in. An attacker might begin with a compromised employee account or exposed device, then use available access to explore other connected systems. This can make a cyberattack harder to spot than a single, isolated intrusion.
Lateral movement is a recognized tactic in cyberattack behavior and may appear during ransomware incidents, data theft, or espionage. Understanding how it works helps organizations look beyond the first compromised device. It also shows why strong identity controls, network visibility, and quick incident response matter.
Where Lateral Movement Fits in a Cyberattack
An attack often starts with an initial access method, such as a stolen password, a vulnerable service, or a malicious attachment. Once inside, the attacker may try to maintain access and learn how the environment is organized. Lateral movement can follow as they seek additional accounts, devices, or network areas.
Attackers may first perform discovery to understand which systems are reachable and what privileges are available. They may then use legitimate credentials, remote services, or other access paths to move between systems. These actions can resemble normal administration, which is one reason defenders need context, not just isolated alerts.
Lateral movement is not always a single event. It may involve a sequence of attempts over hours, days, or longer, as an attacker builds access and pursues a goal. Some intrusions remain quiet while others become disruptive quickly, depending on the attacker’s purpose and the organization’s response.
How Attackers Move Between Systems
Attackers may use credentials that were stolen, guessed, reused, or obtained from a compromised device. If an account has access to multiple systems, it can offer a route deeper into the environment. Overprivileged accounts can make this risk greater because one compromised identity may provide access far beyond its normal role.
Remote administration tools and services can also be misused. These tools are designed to help IT teams manage devices, but attackers may take advantage of them when they have valid access. The activity may appear routine unless security teams check whether the account, device, timing, and destination fit expected behavior.
Another path can involve exploiting a weakness in a system that is reachable from an already compromised device. Attackers may also transfer tools or use built-in utilities to avoid drawing attention. The exact techniques vary, but the underlying objective is to extend access across the network without being stopped.
Common Goals of Lateral Movement
An attacker may move laterally to find data worth stealing, such as customer records, financial information, intellectual property, or confidential business files. Reaching a file server or database may be more valuable than controlling the first device they compromised. Broader access can also help them identify where important information is stored.
Some attackers seek privileged accounts or administrative systems. Greater permissions may let them change security settings, access more devices, or disrupt normal operations. In a ransomware incident, expanding access can help the attacker affect more systems, making recovery more difficult and increasing pressure on the organization.
Other intrusions focus on persistence or surveillance. An attacker may try to maintain access to several systems so that losing one foothold does not end the operation. They may also seek to monitor communications, gather credentials, or understand how an organization works before taking further action.
Why Lateral Movement Is a Serious Security Risk
A breach that begins on one device can become an organization-wide incident if the attacker reaches additional systems. The impact may include unauthorized access to sensitive data, interrupted services, financial loss, or damage to customer trust. The longer suspicious activity goes unnoticed, the more opportunities an attacker may have to expand access.
Lateral movement can also complicate incident response. Security teams may need to determine which accounts and devices were affected, whether access remains active, and what information may have been exposed. If logs are incomplete or systems are tightly connected, it can be harder to establish the full scope of an intrusion.
The risk is not limited to large enterprises. Small businesses can also have connected devices, shared accounts, remote access tools, and critical data. A single compromised account may create an unexpected path into email, cloud services, or business applications if access controls are weak.
Example of Lateral Movement in a Business Network
Imagine an employee receives a convincing message and enters their password on a fake login page. An attacker then uses the stolen account to access the employee’s email. While reviewing accessible resources, the attacker notices shared folders and systems the account can reach.
If the employee’s account has broad permissions or uses the same password elsewhere, the attacker may gain access to additional services. They could then seek systems with more valuable information or access. The original phishing message was the entry point; the movement between accounts and systems is the lateral movement.
This example illustrates why security teams examine more than how an attack began. They need to understand which accounts were used, what systems they accessed, and whether those actions were normal for that user. Limiting access and reviewing unusual activity can help contain an intrusion before it spreads.
Signs Security Teams May Look For
Unusual login patterns can be an early warning sign. Examples include an account accessing systems it does not usually use, logins at unexpected times, or authentication from unfamiliar devices or locations. A single event may have a legitimate explanation, so defenders often assess patterns over time and compare them with normal activity.
Security teams may also investigate unexpected use of remote administration tools, sudden access to many systems, or unusual changes to account permissions. Alerts become more useful when they include context, such as who initiated the action, which device was involved, and whether that behavior fits the person’s role.
Other indicators can include abnormal network connections between internal devices, unexpected file transfers, or security tools being disabled. These signs do not automatically prove that lateral movement is taking place. They are reasons to investigate, correlate relevant logs, and follow the organization’s incident response process.
How Organizations Can Prevent Lateral Movement
Use least privilege so employees and service accounts have only the access required for their work. Review permissions regularly, especially for administrative accounts, shared accounts, and accounts that have changed roles. Reducing unnecessary access can limit the number of systems an attacker can reach if credentials are compromised.
Multi-factor authentication can make stolen passwords harder to use, particularly for remote access and high-impact accounts. Strong account management also includes removing inactive accounts, avoiding shared credentials where possible, and protecting privileged access. These steps reduce the chance that one compromised identity will unlock many parts of the environment.
Network segmentation can restrict unnecessary connections between systems and business areas. Organizations can separate critical assets, limit remote administration paths, and monitor traffic between network zones. Segmentation does not prevent every intrusion, but it can make it harder for an attacker to move freely after gaining initial access.
How to Detect Lateral Movement
Centralized logging helps defenders see activity across endpoints, identity systems, servers, cloud services, and network devices. When records are collected in one place, analysts can connect events that might otherwise appear unrelated. Useful monitoring depends on keeping logs available, protecting their integrity, and deciding which signals deserve investigation.
Endpoint detection and response tools can help identify suspicious behavior on devices, while identity monitoring can flag unusual account activity. Network monitoring may reveal connections that do not fit normal patterns. These tools are most effective when tuned to the organization’s environment and supported by trained analysts who can investigate alerts.
Behavior analytics can help establish what typical access looks like for users, devices, and service accounts. When an account suddenly behaves differently, the change may warrant review. Detection systems should account for legitimate work changes and maintenance, reducing alert fatigue while helping teams notice activity that could indicate account misuse.
What to Do If Lateral Movement Is Suspected
Follow the organization’s incident response plan and alert the security or IT team promptly. Avoid deleting files, wiping devices, or changing settings without guidance, because those actions may destroy evidence or disrupt containment. Keep notes about what was observed and when, using approved reporting channels.
Security responders may isolate affected devices, disable or reset compromised accounts, and review authentication and network logs. They will also assess whether privileged credentials, cloud accounts, or shared systems may be involved. The response should be coordinated so that containment reduces risk without causing unnecessary disruption to critical services.
After the immediate threat is contained, investigate how access began and which controls failed to prevent spread. Restore systems from trusted sources where required, rotate credentials that may have been exposed, and confirm that monitoring is working. A post-incident review can guide improvements to access, segmentation, backups, and response procedures.
Lateral Movement in Cloud and Hybrid Environments
Cloud services and hybrid networks introduce additional identities, applications, and connections to monitor. An attacker may move through cloud accounts, collaboration tools, virtual machines, or links between on-premises systems and cloud platforms. Security teams need visibility across these environments rather than treating each service as a separate island.
Misconfigured permissions or exposed credentials can create routes between cloud resources. Organizations can review identity roles, service accounts, API access, and external sharing settings. Logging should capture important activity across cloud platforms, and teams should know how to investigate suspicious access that crosses between environments.
A hybrid environment can make it harder to understand which team owns a system or log source. Clear responsibilities help close that gap. Businesses should map important dependencies, agree on escalation paths, and test whether their incident response process can account for activity across cloud and on-premises systems.
Common Challenges in Stopping Lateral Movement
One challenge is that attackers may use legitimate tools and credentials. Blocking every remote administration tool is rarely practical, because IT teams rely on some of them to support business operations. Organizations need to control who can use these tools, from which devices, and under what conditions.
Another challenge is limited visibility. Older systems, unmanaged devices, third-party services, or incomplete logs can leave gaps in monitoring. A realistic security program identifies critical blind spots and prioritizes improvements based on risk, instead of expecting every organization to monitor every system equally.
Security teams can also face too many alerts to investigate quickly. Poorly tuned detection creates noise that can obscure meaningful events. Regularly reviewing alert quality, connecting signals across tools, and practising incident response can help teams focus on activity that poses the greatest risk.
Conclusion
Lateral movement in cybersecurity describes how an attacker expands access from one compromised account or device to others inside an organization. It can support data theft, ransomware, surveillance, or broader control of business systems, often by abusing credentials and normal network tools.
Organizations can reduce the risk through least-privilege access, multi-factor authentication, network segmentation, centralized logging, and active monitoring. These controls help limit how far an intruder can move and give defenders a better chance of detecting suspicious behavior early.
If lateral movement is suspected, report it promptly and follow the incident response plan. A coordinated investigation can help contain affected accounts and devices, understand the scope, and strengthen controls. Regular reviews and practice make it easier to respond when an intrusion occurs.
FAQs
What is lateral movement in cybersecurity?
Lateral movement is when an attacker uses access to one compromised account or device to reach other systems inside a network, often to find data or gain broader control.
What is an example of lateral movement?
An attacker steals an employee’s login, accesses their email, and then uses the account’s permissions to reach shared files or additional business systems.
How do attackers move laterally through a network?
They may misuse stolen credentials, remote administration tools, system weaknesses, or existing permissions to access other devices and services.
How can organizations prevent lateral movement?
Use least-privilege access, multi-factor authentication, network segmentation, strong account management, and monitoring for unusual identity and system activity.
Is lateral movement always part of a cyberattack?
No. It describes a tactic used in some intrusions after initial access. Attackers may use it to expand access, but not every cyberattack involves movement between systems.