

What Is Network Segmentation?
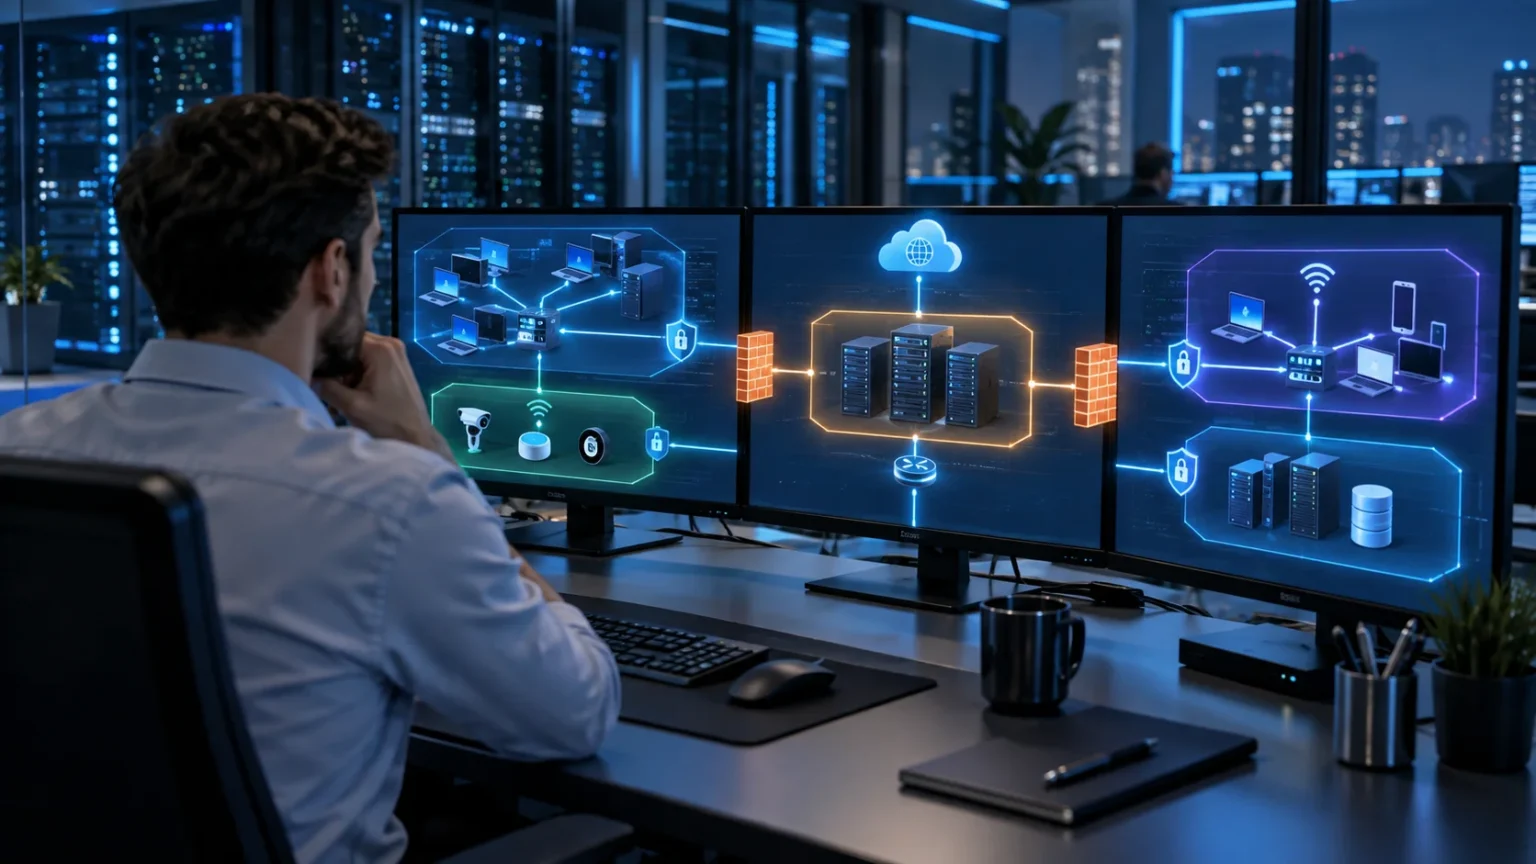
Network segmentation is the practice of dividing a larger computer network into smaller, separate sections. Each section can contain specific users, devices, servers, or applications based on their purpose or security requirements. Instead of allowing every connected device to communicate freely, segmentation creates boundaries that control how traffic moves between different parts of the network.
These smaller sections are commonly called network segments, subnets, or zones. Security rules can determine which segments are allowed to communicate and what types of traffic can pass between them. This structure gives administrators more control over network access while helping reduce unnecessary communication between systems that do not need to interact.
Network segmentation is widely used in businesses, data centers, cloud environments, and even advanced home networks. It can improve cybersecurity, performance, and network management when configured properly. The basic idea is simple: important systems should not automatically be accessible to every person or device simply because they share the same overall network.
How Does Network Segmentation Work?
Network segmentation works by creating logical or physical boundaries between different groups of connected devices. Administrators may separate employee computers, servers, printers, guest devices, security cameras, and other systems into their own network areas. Traffic moving from one segment to another can then be inspected and controlled using predefined access rules.
Routers, switches, firewalls, virtual local area networks, and software-defined networking tools can all play roles in segmentation. The exact technology depends on the size and complexity of the environment. Smaller organizations may use VLANs and firewall rules, while large enterprises may combine several technologies to create more detailed security zones.
Once segments are created, administrators define which connections are permitted. For example, employees may be allowed to access a business application server while guest Wi-Fi users are blocked from reaching internal systems. This controlled communication reduces unnecessary exposure and makes network behavior easier to monitor and manage.
Why Is Network Segmentation Important?
One of the biggest reasons organizations use network segmentation is security. A flat network allows many devices to communicate with one another freely, which can increase the impact of a compromised account or device. Segmentation introduces barriers that may prevent unauthorized access from spreading easily across the entire network.
Segmentation can also make network management more organized. Administrators can group systems based on departments, functions, security needs, or geographic locations. This makes it easier to apply appropriate rules to specific groups rather than creating one large set of permissions for every device connected to the network.
Performance can sometimes improve as well because unnecessary broadcast traffic can be limited to smaller network areas. Devices do not always need to receive information intended for completely unrelated systems. By creating smaller broadcast domains, network segmentation can help reduce unwanted traffic and make network behavior more predictable.
Network Segmentation and Cybersecurity
Cybersecurity is one of the most important use cases for network segmentation. If an attacker compromises one computer on a completely open network, that system may provide opportunities to reach other devices. Segmentation can restrict that movement by limiting which resources the compromised computer is permitted to contact.
This approach helps reduce what is often called lateral movement. Lateral movement occurs when an attacker uses one compromised device or account to explore and access additional systems inside a network. Well-designed segmentation creates additional security boundaries that an attacker must overcome instead of allowing unrestricted internal communication.
Segmentation does not make a network completely secure on its own. Strong passwords, authentication, endpoint protection, patching, monitoring, and other cybersecurity controls are still important. However, segmentation adds another layer of protection by limiting access and reducing the number of systems exposed when one part of the network experiences a security problem.
What Is a Flat Network?
A flat network is an environment where most connected devices exist within the same broad network area and can communicate with little internal restriction. This architecture can be simple to set up and manage in very small environments. However, the lack of internal boundaries can become a security and management problem as the network grows.
Imagine an organization where employee laptops, printers, servers, cameras, and guest devices are all connected to the same network. If communication is not restricted, a compromised guest device may have unnecessary visibility into business systems. This creates more opportunities for scanning, unauthorized access, or other unwanted network activity.
Segmentation transforms this flat structure into smaller controlled areas. Guest devices might receive internet access only, while servers remain inside a protected internal segment. The result is a more organized network where access depends on business requirements rather than simply whether a device has successfully connected.
Common Types of Network Segmentation
Physical segmentation separates network areas using different hardware, cables, switches, or other infrastructure. Systems in separate physical networks cannot communicate unless a device such as a router or firewall connects them. This approach can provide strong separation but may require additional equipment and become expensive in larger environments.
Logical segmentation creates separation using configuration rather than completely independent hardware. VLANs, subnets, firewall rules, and software-defined networking technologies can divide one physical infrastructure into several logical areas. This approach is widely used because it provides flexibility without requiring entirely separate equipment for every network segment.
Organizations can also create security zones based on purpose. Common examples include guest networks, employee networks, server zones, management networks, and environments for Internet of Things devices. The technology may vary, but the goal remains consistent: systems with different purposes and risk levels should not automatically receive identical network access.
VLANs and Network Segmentation
A VLAN, or virtual local area network, allows administrators to logically group devices even when those devices connect through the same physical networking equipment. Devices assigned to different VLANs can be treated as though they belong to separate networks. This makes VLANs a common tool for implementing network segmentation.
For example, an organization might place employees in one VLAN, printers in another, and security cameras in a third. Traffic between these VLANs can then pass through routing or firewall controls. Administrators can decide exactly which types of communication should be permitted rather than allowing every device to communicate freely.
VLANs provide separation, but they should not automatically be considered a complete security solution. Proper routing rules, firewall policies, access controls, and secure switch configuration are also important. Poorly configured VLANs can still expose sensitive resources, so segmentation needs to be designed around clear security requirements.
Network Segmentation With Firewalls
Firewalls are commonly used to control communication between network segments. They examine traffic and apply rules that determine whether a connection should be allowed or blocked. This makes them particularly useful when sensitive systems need stronger protection from less trusted devices or network areas.
An organization might place important database servers inside a protected segment and allow only approved application servers to communicate with them. Employee devices could be prevented from making direct database connections. These restrictions reduce unnecessary access while still allowing the applications employees need to function properly.
Firewall rules should be kept as specific as practical. Allowing every type of traffic between two segments weakens the purpose of creating separate zones. Administrators should understand which systems actually need to communicate, what protocols they require, and whether access should be limited to particular users, devices, or applications.
Network Segmentation for Home Networks
Network segmentation can also be useful at home, especially as households connect more smart devices. Laptops, phones, smart televisions, security cameras, speakers, appliances, and other Internet of Things devices may all share the same router. Separating some of these devices can reduce unnecessary access to computers containing personal information.
A common example is creating a guest Wi-Fi network for visitors. Guests can access the internet without receiving the same level of access as trusted household devices. Some routers also offer dedicated IoT networks, allowing smart home products to remain separate from laptops, storage devices, and other sensitive equipment.
Large homes may combine network organization with wider wireless coverage. People comparing mesh Wi-Fi systems should check whether the equipment supports guest networks, IoT separation, VLANs, or other access controls. Strong Wi-Fi coverage is useful, but managing which devices can communicate can improve the overall network design.
Benefits of Network Segmentation
Improved security is the most obvious benefit. When systems are separated according to their function and risk level, unauthorized access to one segment does not automatically provide unrestricted access everywhere else. This can reduce the potential impact of malware, compromised credentials, or an infected device connected to the network.
Segmentation also supports clearer access control. Finance employees, developers, guests, administrators, and IoT devices do not necessarily need identical access to internal resources. Separating these groups makes it easier to apply permissions that reflect what each user or device actually needs to perform its intended function.
Troubleshooting and monitoring may become easier as well. When traffic is divided into smaller logical areas, administrators can more easily identify where unusual activity is occurring. Network problems can sometimes be isolated to one segment instead of affecting or confusing the entire environment, making investigation more focused.
Challenges of Network Segmentation
Network segmentation adds complexity because administrators must understand how systems communicate before separating them. Blocking necessary connections can interrupt business applications, printing, authentication, file access, or other services. Careful planning is therefore important before introducing new firewall rules, VLANs, or routing restrictions into an existing network.
Poor documentation can create additional problems over time. If no one remembers why a certain rule exists, administrators may hesitate to remove it or accidentally create duplicate permissions. Clear records of network zones, allowed connections, business purposes, and responsible teams make segmented environments easier to manage.
Over-segmentation can also make a network unnecessarily complicated. Creating a separate segment for every individual system may add management overhead without providing enough additional security benefit. A useful design balances security with practical administration by grouping systems according to meaningful risk levels, functions, and communication requirements.
Network Segmentation vs Microsegmentation
Traditional network segmentation usually divides a network into relatively broad areas such as departments, server networks, or security zones. Devices within one segment may still communicate fairly freely. This approach can significantly improve security compared with a completely flat network while remaining manageable for many organizations.
Microsegmentation applies more detailed controls between individual workloads, applications, or systems. Instead of assuming everything inside one network zone can communicate, microsegmentation can restrict connections at a much smaller level. This approach is often associated with data centers, virtual environments, cloud infrastructure, and zero-trust security strategies.
Neither approach is automatically suitable for every environment. Traditional segmentation may provide enough control for smaller organizations, while complex cloud or enterprise environments may benefit from more granular policies. The appropriate level of segmentation depends on risk, network architecture, available management tools, and how systems need to communicate.
Best Practices for Network Segmentation
Begin by understanding the devices, applications, users, and data present on your network. You cannot create effective boundaries without knowing which systems need to communicate. Document important connections first so segmentation rules protect sensitive resources without unexpectedly interrupting normal business operations.
Apply the principle of least privilege whenever possible. A network segment should receive only the access required for its legitimate purpose. Guest devices, for example, usually need internet access but not direct access to internal servers, while administrators may require broader permissions that should remain unavailable to ordinary users.
Review segmentation rules regularly as the network changes. New applications, cloud services, devices, and employee roles can make older access policies outdated. Monitoring traffic can also reveal unnecessary connections or attempted communication between segments, helping administrators refine policies and identify potentially suspicious behavior.
How to Plan a Network Segmentation Strategy
Start by identifying the most important or sensitive assets on the network. These may include databases, financial systems, administrative interfaces, customer information, backup infrastructure, or critical business applications. Protecting high-value systems provides a logical starting point for deciding where stronger security boundaries should exist.
Next, group devices according to function and trust level. Employee workstations, servers, guests, printers, IoT products, management interfaces, and development systems may each require different access. Mapping these relationships visually can help administrators understand which connections are necessary before creating technical segmentation policies.
Finally, introduce changes gradually rather than redesigning an entire network at once. Test firewall rules and VLAN configurations carefully, monitor traffic, and confirm important applications still function. A staged approach makes troubleshooting easier and reduces the chance that a segmentation change unexpectedly disrupts important users or services.
Conclusion
Network segmentation divides a larger network into smaller controlled sections so administrators can manage communication more precisely. Instead of allowing every connected system to interact freely, segmentation creates boundaries between users, devices, servers, applications, and security zones. This makes networks easier to organize and can reduce unnecessary exposure.
Technologies such as VLANs, subnets, routers, and firewalls can all support network segmentation. The exact design depends on the size of the network, security requirements, and how systems need to communicate. Effective segmentation focuses on meaningful boundaries rather than simply creating as many separate networks as possible.
For both businesses and advanced home networks, segmentation can improve security, access control, monitoring, and organization. However, good planning is essential because overly restrictive or poorly documented rules can create operational problems. The strongest approach combines thoughtful segmentation with broader cybersecurity practices such as authentication, patching, monitoring, and endpoint protection.
FAQs
What is network segmentation in simple terms?
Network segmentation means dividing one large network into smaller sections. Access between those sections can then be controlled so users and devices communicate only with the systems they genuinely need.
What is the main purpose of network segmentation?
The main purpose is to control network communication and reduce unnecessary access. It can improve security, limit lateral movement, simplify management, and reduce the potential impact of a compromised device.
What is an example of network segmentation?
A business might separate employee computers, guest Wi-Fi, servers, and security cameras into different network segments. Firewall rules can then decide which groups are allowed to communicate with one another.
Are VLANs the same as network segmentation?
VLANs are one technology used to create logical network segments, but segmentation is the broader concept. Firewalls, subnets, routers, physical networks, and software-defined controls can also be used for segmentation.
Does network segmentation improve security?
Yes, properly designed segmentation can improve security by restricting unnecessary communication between systems. It can limit an attacker’s ability to move across a network, although other security controls are still necessary.



